Cybersecurity has become an essential part of modern business operations. Organizations today rely on cloud platforms, digital applications, connected devices, remote services, and large volumes of data. As technology expands, security teams must manage not only cyber threats but also policies, compliance requirements, access controls, risk, and security processes.
This is where Cybersecurity governance automation toronto becomes an important area of study for aspiring cybersecurity professionals. Governance automation combines security management with technology-driven workflows that can reduce repetitive tasks, improve visibility, and support more consistent security practices.
For learners interested in enterprise technology, Canadian College for higher studies provides an educational environment where cybersecurity, governance, automation, cloud technologies, and related IT concepts can be explored through structured learning. Its Post-Graduate Diploma in Enterprise Cybersecurity & Governance Automation includes areas such as security governance frameworks, cloud environments, automation, SIEM, identity management, DevSecOps, and compliance.
What Is Cybersecurity Governance?
Cybersecurity governance refers to the policies, procedures, responsibilities, and controls an organization uses to manage cybersecurity risks. It ensures that security is not viewed only as a technical IT function but is connected with wider business operations.
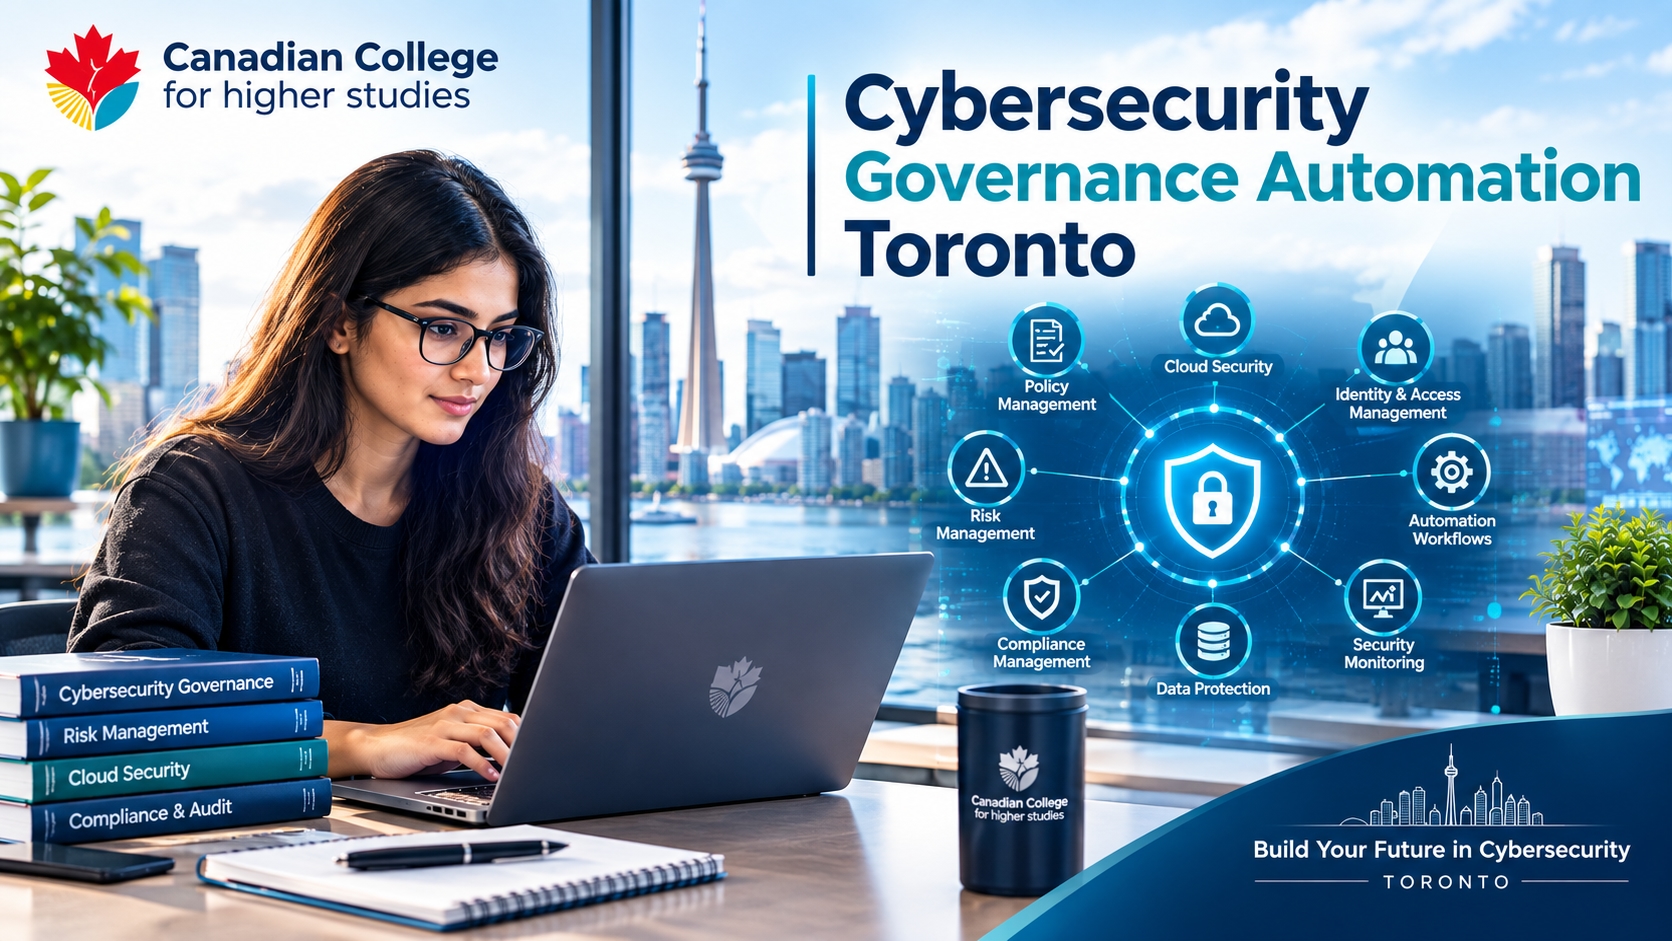
A governance framework may cover:
Security policies and procedures
Risk identification and assessment
Access control
Compliance management
Incident response
Security monitoring
Data protection
Employee security awareness
Third-party risk management
A structured governance approach helps organizations establish accountability and determine how security activities should be managed. The source material for this article similarly emphasizes that governance provides a framework for protecting information and technology resources while defining responsibilities and monitoring security performance.
Why Cybersecurity Governance Matters
Modern organizations continuously introduce new software, cloud services, applications, devices, and digital processes. Without appropriate governance, security controls can become inconsistent or difficult to monitor.
Governance helps organizations determine who is responsible for security activities, how risks should be evaluated, and how security performance should be tracked. It can also support the documentation needed for internal policies, audits, and applicable compliance requirements.
This connection between cybersecurity, enterprise risk, and governance is also reflected in professional education in Toronto. For example, the University of Toronto School of Continuing Studies describes enterprise IT risk management as involving strategic and operational cyber risks, risk mitigation, compliance, and alignment between cybersecurity and enterprise risk management.
What Is Cybersecurity Governance Automation?
Cybersecurity governance automation toronto describes the growing use of software, workflows, scripting, cloud technologies, and intelligent systems to automate repetitive governance and security activities.
Instead of depending entirely on spreadsheets, emails, and manual reviews, organizations can use automated systems to collect information, monitor controls, identify potential risks, organize evidence, and notify responsible teams.
For example, an automated workflow could identify a security control that no longer meets an established requirement and create a task for the appropriate team. Similarly, automated processes can help collect compliance evidence from connected systems and organize it for review.
Automation does not eliminate cybersecurity professionals. Instead, it can allow them to spend more time on investigation, analysis, decision-making, risk management, and strategic planning. The provided source specifically highlights automation as a way to reduce repetitive work while maintaining the importance of human oversight.
Key Benefits of Governance Automation
1. Improved Efficiency
Security and compliance teams can spend considerable time reviewing information, collecting evidence, updating records, and preparing reports.
Automation can streamline these repetitive activities through predefined workflows. This may help organizations manage routine governance tasks more efficiently and allow professionals to focus on higher-value security activities.
2. Better Risk Visibility
Modern organizations generate security information across networks, applications, endpoints, cloud environments, and other systems.
Automated platforms can collect information from multiple sources and present it through centralized dashboards. This can help security teams identify vulnerabilities, policy violations, unusual activity, and potential compliance gaps more efficiently.
3. More Consistent Security Processes
Manual processes can sometimes produce inconsistent results. Automated workflows can apply predefined rules in a repeatable manner.
For example, when a new employee joins an organization, an automated workflow can initiate access requests, approval steps, and security checks according to established policies.
4. More Structured Compliance Reporting
Compliance activities can require organizations to collect and organize substantial amounts of evidence.
Automation can help gather relevant information and maintain records in a more structured way. This can reduce some of the administrative effort involved in preparing compliance documentation.
5. Faster Security Workflows
Automated systems can trigger notifications or predefined actions when specific security conditions occur. For example, a workflow could alert a security team when a critical control fails or a defined risk threshold is exceeded.
The goal is not to make every security decision automatically, but to help teams recognize and process important events more efficiently.
Technologies Used in Governance Automation
Security Information and Event Management
Security Information and Event Management, commonly known as SIEM, brings together security-related events from different sources. Security teams can analyze this information to identify suspicious patterns and investigate potential incidents.
SIEM becomes particularly useful when organizations generate large volumes of data across servers, applications, networks, and cloud environments. The CCHS program also includes SIEM tools and AI-driven detection within its curriculum.
Security Orchestration and Automation
Security Orchestration, Automation and Response, or SOAR, can connect security tools and automate predefined workflows.
A workflow might collect information about a suspicious event, organize relevant details, and send the information to the appropriate security team for investigation.
Governance, Risk and Compliance Platforms
GRC platforms support activities involving governance requirements, risks, controls, audits, and compliance.
When integrated with automation, these platforms can help reduce manual evidence collection and provide centralized visibility into organizational controls and risks.
Artificial Intelligence and Machine Learning
AI and machine learning can assist cybersecurity teams by analyzing large volumes of information and identifying patterns.
These technologies may support threat detection, anomaly identification, risk analysis, and prioritization. However, human oversight remains important because automated systems can produce incomplete or inaccurate results. The provided source also emphasizes the continuing role of human judgment when AI-supported security technologies are used.
Why Ontario Is Relevant to Cybersecurity Governance
Ontario has organizations across finance, healthcare, education, manufacturing, retail, professional services, and technology. These organizations operate increasingly complex digital environments involving cloud services, applications, identities, devices, data, and third-party systems.
As a result, cybersecurity professionals may need knowledge that extends beyond traditional network defense. Understanding governance, risk management, compliance, automation, and cloud security can provide a broader view of how enterprise security programs operate.
For learners researching Cybersecurity governance automation toronto, this combination of technical and governance knowledge can be particularly relevant to understanding modern enterprise environments.
Toronto also has educational opportunities covering cybersecurity risk, governance, and compliance. In addition to specialized programs, institutions such as the University of Toronto offer courses addressing enterprise cybersecurity risk management and governance-related topics.
Skills Students Can Develop
A career in cybersecurity governance automation requires a combination of technical knowledge, analytical ability, and an understanding of organizational processes.
Cybersecurity Fundamentals
Students can build knowledge of networks, operating systems, authentication, encryption, vulnerabilities, and common cyber threats. These fundamentals provide a foundation for understanding more advanced security technologies.
Risk Management
Risk management involves identifying, evaluating, prioritizing, and managing cybersecurity risks. It also connects technical security decisions with broader organizational objectives.
Governance and Compliance
Students can explore how policies, security controls, audits, frameworks, and regulatory requirements influence enterprise cybersecurity programs.
Automation and Cloud Skills
Automation skills can include scripting, workflow design, infrastructure automation, and cloud technologies. The CCHS program, for example, lists Python and shell programming, cloud administration, Terraform, Ansible, Git, policy-as-code, and DevSecOps governance automation among its program components.
Analytical Thinking
Cybersecurity professionals frequently investigate unusual events, assess risks, review evidence, and make informed decisions. Analytical thinking is therefore useful across both technical and governance-focused positions.
Career Areas in Cybersecurity Governance
Knowledge of governance and automation can be applied across several cybersecurity career areas. Potential roles mentioned by the source material include:
Cybersecurity Analyst
Security Operations Analyst
GRC Analyst
IT Risk Analyst
Compliance Analyst
Security Administrator
Cloud Security Professional
Security Automation Specialist
Cybersecurity Consultant
The exact responsibilities and requirements differ between organizations. Some positions may be highly technical, while others concentrate more heavily on governance, risk, compliance, auditing, or organizational security processes.
How Education Can Support Your Cybersecurity Career
Cybersecurity requires both theoretical understanding and practical exposure. Students can benefit from learning environments that connect security concepts with real-world technologies, scenarios, and workflows.
Canadian College for higher studies offers a Post-Graduate Diploma in Enterprise Cybersecurity & Governance Automation that covers enterprise cybersecurity, governance frameworks, compliance, automation, cloud systems, identity and access management, SIEM, DevSecOps, and related technologies. The program is listed as 1,570 hours with online synchronous and asynchronous delivery and cloud-based lab access.
Why Practical Learning Matters
Reading about cybersecurity concepts is useful, but practical activities can make those concepts easier to understand. Working with security tools, analyzing scenarios, exploring governance workflows, and examining risk-management processes can help learners connect theory with practical applications.
The source material also highlights the value of practical exposure and continued learning because cybersecurity technologies and threats change frequently.
Challenges of Governance Automation
Automation offers important advantages, but it also introduces challenges.
Poorly designed workflows can generate unnecessary alerts or cause important activities to be missed. Automated systems also depend on accurate information. If connected systems provide incomplete or outdated data, automated processes may not produce reliable results.
Organizations must therefore consider:
Data accuracy
Privacy
Access permissions
System integration
Workflow design
Human oversight
Security testing
Automation should support cybersecurity professionals rather than replace responsible decision-making.
The Future of Cybersecurity Governance Automation
The future of enterprise security is likely to involve closer integration between automation, cloud computing, artificial intelligence, identity management, and governance platforms.
Organizations are continuing to look for ways to reduce repetitive work while improving visibility and compliance management. Automated workflows may increasingly connect security operations, cloud environments, identity systems, risk management, and compliance processes.
For students exploring Cybersecurity governance automation toronto, this evolving environment creates an opportunity to develop a combination of technical and governance-oriented knowledge.
The future will not depend on technology alone. Organizations will continue to require professionals who understand business requirements, security risks, ethical considerations, governance responsibilities, and the limitations of automated systems.
Conclusion
Cybersecurity governance automation brings together cybersecurity, risk management, compliance, technology, and automated workflows. It can help organizations create more consistent security processes, improve visibility, reduce repetitive administrative work, and respond more efficiently to security concerns.
For students and aspiring professionals, learning about Cybersecurity governance automation toronto can provide insight into how modern organizations approach security beyond traditional technical defenses. Developing knowledge in governance, risk management, cloud security, automation, compliance, and cybersecurity fundamentals can create a strong foundation for continued professional development.
With structured education and practical learning, Canadian College for higher studies can help learners explore the technical and governance concepts associated with modern enterprise cybersecurity. Its curriculum includes areas such as governance automation, policy-as-code, cloud security, SIEM, identity management, and DevSecOps.
As organizations continue their digital transformation, professionals who can understand both cybersecurity technologies and governance processes will remain an important part of modern security teams. Building these skills through education, hands-on practice, continuous learning, and real-world scenarios can help learners prepare for the changing demands of the cybersecurity field.