Information technology companies operate in an environment where data, applications, infrastructure, and digital services are central to everyday business. A security incident affecting any of these assets can potentially disrupt operations, expose sensitive information, or damage customer confidence.
For this reason, cybersecurity cannot be treated solely as a technical responsibility. Organizations need a structured approach that connects technology controls with business risks, responsibilities, processes, and continual improvement.
This is where ISO/IEC 27001 can provide value. By establishing an Information Security Management System (ISMS), an IT company can create a systematic framework for identifying information-security risks and determining how those risks should be managed.
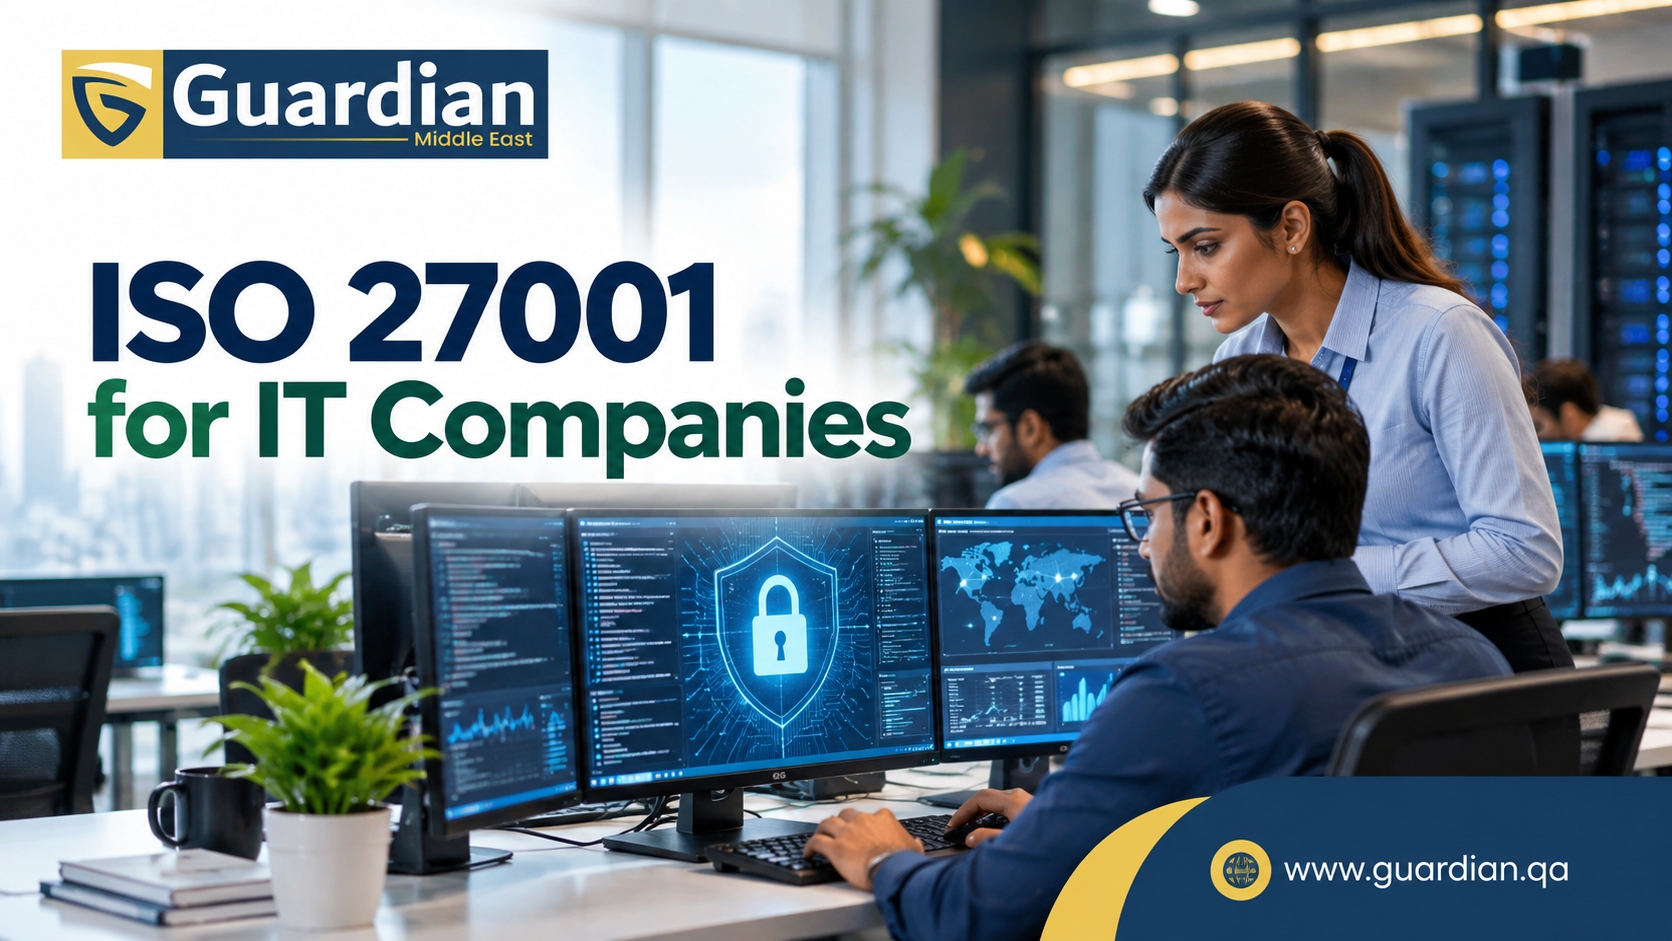
Why IT Companies Face Complex Information Security Risks
IT organizations can face a wide range of risks because they often manage information belonging to multiple stakeholders.
Typical information assets may include:
Customer and employee information
Source code and intellectual property
Cloud infrastructure
Databases and application environments
Authentication credentials
Financial and contractual information
Security logs and monitoring data
Third-party service information
The risk environment can become even more complex when organizations use remote work, cloud platforms, software-as-a-service applications, outsourced development, and external technology vendors.
A firewall or endpoint protection platform alone cannot address all these risks. Effective security also depends on governance, employee awareness, supplier management, access controls, incident response, and business continuity.
What Is an Information Security Management System?
An ISMS is a systematic approach to managing information security within an organization.
ISO/IEC 27001 provides requirements for establishing, implementing, maintaining, and continually improving an ISMS. Rather than prescribing one universal collection of security tools, the standard encourages organizations to consider their own context, information-security risks, and appropriate controls.
This risk-based approach is particularly relevant to IT companies because two organizations with similar technologies may have very different information-security risks.
For example, a cloud service provider handling healthcare information may have different priorities from a software development company building an internal business application.
Risk Assessment as the Foundation
One of the most important elements of an effective ISMS is understanding information-security risk.
An IT company can begin by identifying important information assets, considering potential threats and vulnerabilities, assessing the consequences of security incidents, and determining how risks should be treated.
Risk treatment may involve:
Implementing security controls
Avoiding certain activities
Transferring specific risks
Accepting risks under defined conditions
The objective is not necessarily to eliminate every conceivable risk. Instead, the organization should make informed decisions about risks and implement appropriate measures based on its context and objectives.
Access Control and Identity Management
Unauthorized access remains a significant concern for IT organizations.
An ISMS can support a structured approach to identity and access management by establishing appropriate responsibilities and controls.
Organizations may consider questions such as:
Who should have access to specific systems?
Is access based on business requirements?
Are privileged accounts appropriately controlled?
Are user permissions reviewed periodically?
How are accounts removed when employees leave?
Are authentication mechanisms appropriate for the risk?
These questions connect technical identity controls with organizational processes.
Managing Third-Party and Cloud Risks
IT companies frequently depend on external providers for cloud hosting, software platforms, development services, infrastructure, and other capabilities.
Third-party relationships can introduce additional security risks.
Organizations should therefore consider security requirements when selecting and managing suppliers. Depending on the nature of the relationship, this may involve evaluating supplier security practices, contractual requirements, access arrangements, incident notification expectations, and ongoing performance.
Cloud adoption does not remove the organization's responsibility for managing information-security risks. Instead, organizations need to understand which security responsibilities belong to the cloud provider and which remain with the customer.
Incident Response and Business Continuity
Even well-designed security controls cannot guarantee that incidents will never occur.
An IT organization should therefore consider how it will detect, respond to, and recover from information-security incidents.
An effective incident-management approach can establish:
How incidents are identified and reported
Who is responsible for responding
How incidents are assessed and prioritized
How affected systems are contained
How recovery activities are coordinated
How lessons learned are incorporated into improvements
Business continuity is closely connected to information security. Organizations providing critical IT services should understand which processes and services need to remain available and how they will respond when normal operations are disrupted.
Employees Are Part of the Security System
Technology controls can be weakened when employees do not understand their security responsibilities.
Security awareness should therefore be incorporated into the organization's broader information-security approach.
Employees may need guidance on areas such as:
Password and authentication practices
Phishing and social engineering
Handling confidential information
Reporting suspicious activity
Remote-working security
Use of company devices and systems
The objective is to make security responsibilities part of everyday organizational behavior rather than treating cybersecurity as the responsibility of the IT department alone.
Internal Audits and Continual Improvement
An ISMS should not remain static.
Organizations can use internal audits, management reviews, monitoring, incident analysis, and corrective actions to identify opportunities for improvement.
For an IT company, this could mean reviewing whether security controls remain appropriate as technologies, customers, threats, regulations, and business processes change.
Certification, where pursued, involves an independent certification body assessing conformity with the applicable requirements. Organizations should distinguish this independent certification activity from consulting or implementation support.
A Practical Example
Consider an IT company that provides cloud-based business software to several corporate customers.
The company stores customer information in a cloud environment and allows developers, administrators, and support personnel to access different systems.
An ISMS approach could help the organization systematically consider:
Which customer information requires protection
Which employees need access
How privileged access is controlled
How cloud suppliers are evaluated
How security incidents are reported
How customer data is protected
How service interruptions are handled
How security performance is reviewed
The value comes from connecting these activities into a structured management system rather than managing them as isolated technical tasks.
When Should an IT Company Consider ISO 27001?
ISO/IEC 27001 may be particularly relevant to organizations that manage sensitive information, provide technology services, operate cloud platforms, handle customer data, or need to demonstrate a structured approach to information-security management.
Organizations considering certification should first understand their business context, information-security risks, applicable requirements, and certification scope.
A useful starting point for organizations exploring ISO 27001 certification is this ISO certification resource.
Conclusion
Cybersecurity requires more than implementing individual security technologies. IT companies need a management approach that connects people, processes, technology, risk management, and business objectives.
ISO/IEC 27001 provides a framework for establishing an Information Security Management System that can help organizations systematically manage information-security risks and continually improve their security practices.
For IT organizations, the real value of an ISMS lies not simply in achieving certification, but in developing a repeatable approach to understanding risks, protecting information, responding to incidents, and adapting as the digital environment changes.
Discussion Questions
What is the biggest challenge organizations face when implementing an ISMS?
How can IT companies balance security requirements with operational efficiency?
What role should senior management play in information-security risk management?
How frequently should organizations reassess their information-security risks?