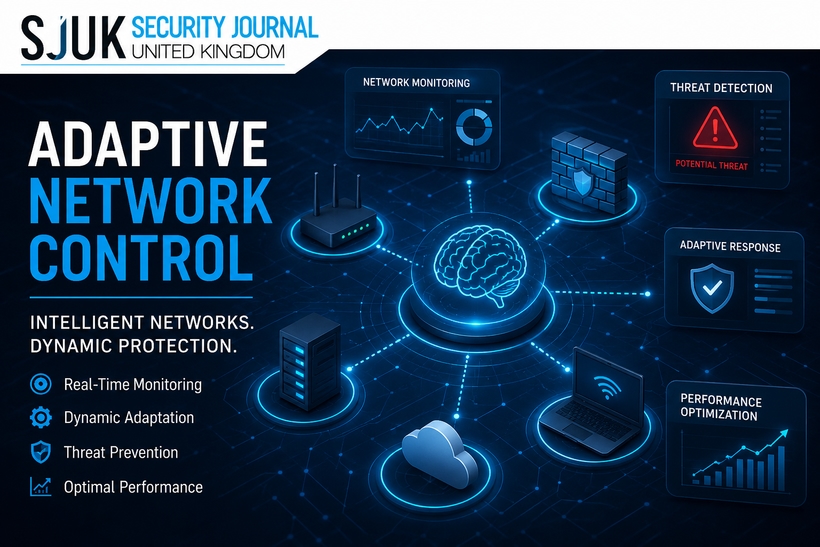
Network environments are constantly changing as organisations adopt cloud services, remote working, connected devices and new digital technologies. At the same time, cyber threats continue to evolve, creating challenges for security teams that rely on fixed network controls, provides an approach that allows network security measures to adjust according to changing conditions, traffic patterns and potential risks. Instead of relying entirely on static rules, adaptive controls can use continuous monitoring and contextual information to support more responsive security decisions.
Understanding how this approach works can help organisations consider ways to improve network visibility, threat detection and security response.
What Is Adaptive Network Control?
Understanding adaptive network control starts with recognising how networks can adjust their security controls when conditions or risks change.
Its refers to the use of dynamic policies and controls that can change in response to network activity, user behaviour, device conditions or security events.
Traditional network controls may operate according to predefined rules that remain unchanged until an administrator modifies them. Adaptive approaches can incorporate information from ongoing monitoring to determine whether a particular connection, device or activity requires a different level of control.
For example, if a device that normally communicates with a limited number of internal systems suddenly generates unusual traffic, an adaptive security system may increase monitoring or restrict its access based on the organisation's policies.
The exact capabilities depend on the technologies being used, but the general objective is to make network security more responsive to changing circumstances.
Why Are Network Threats Becoming More Dynamic?
Modern cyber threats can change rapidly, making continuous visibility and flexible security controls increasingly important.
Organisations now operate networks that can include on-premises infrastructure, cloud platforms, remote users, mobile devices, IoT systems and third-party services. This creates a larger and more varied environment for security teams to monitor.
Attackers can also change their techniques during an intrusion. They may use compromised accounts, unusual traffic patterns, malicious software or legitimate tools to move through an environment.
Remote and hybrid working can further complicate network security because users may connect from different locations and devices.
These changes mean that a security decision that was appropriate earlier may not remain appropriate later. Adaptive network control can help organisations respond to changes by continuously evaluating network conditions rather than depending solely on fixed assumptions.
How Does Adaptive Network Control Respond to Changing Network Threats?
Adaptive network control can respond to changing threats by continuously assessing network activity and adjusting security controls when predefined risk conditions are reached.
Real-Time Network Monitoring
Continuous monitoring provides visibility into network traffic, connected devices, users and other activity.
Security teams can establish expected patterns and identify significant deviations from normal behaviour. For example, an unexpected increase in outbound traffic from a device could trigger additional investigation.
Monitoring does not automatically mean that every unusual event represents an attack. Instead, it provides information that can be used to assess whether further action is appropriate.
Dynamic Policy Adjustment
Adaptive systems can adjust network policies according to defined conditions.
For example, an organisation could apply stricter access controls to a device that fails a security check or displays behaviour associated with increased risk.
Policies may consider factors such as user identity, device status, location, application activity and the sensitivity of the requested resource.
This can allow security controls to reflect current circumstances rather than treating every connection identically.
Threat Detection and Analysis
Adaptive network control can work alongside threat detection technologies to identify suspicious activity.
Security platforms may analyse traffic, authentication events, endpoint information and other security signals to identify behaviour that requires attention.
When relevant indicators are detected, the organisation's policies can determine whether to increase monitoring, require additional verification or restrict access.
Automated Response
Automation can help security teams respond more quickly to certain predefined events.
Depending on the organisation's configuration, automated actions may include restricting a connection, isolating a device, blocking particular traffic or requiring additional authentication.
Automated responses should be carefully tested because incorrect decisions can disrupt legitimate business activity.
Continuous Risk Assessment
Risk can change as users, devices and network conditions change.
An adaptive approach can continuously reassess these factors and adjust controls when appropriate. A device that was considered low risk earlier in the day may require additional scrutiny if its behaviour changes significantly.
This ongoing assessment is particularly useful in environments where users and devices frequently connect and disconnect.
Key Technologies Supporting Adaptive Network Control
Adaptive network control depends on technologies that provide accurate visibility, contextual information and the ability to apply security policies.
Network Monitoring and Traffic Analysis
Network monitoring tools provide information about traffic flows, devices and communication patterns.
Artificial Intelligence and Machine Learning
AI and machine learning can assist with identifying patterns and anomalies within large volumes of network data. Their effectiveness depends on the quality of available data, system configuration and human oversight.
Security Information and Event Management
Security information and event management platforms can collect and correlate security events from different systems, helping security teams identify activity that may require investigation.
Identity and Access Management
Identity and access controls can help determine who is requesting access and whether that access is appropriate for the current circumstances.
Network Segmentation
Segmentation separates different parts of a network so that access to sensitive systems can be restricted. Adaptive controls can potentially adjust access between segments based on defined risk conditions.
Zero Trust Security Principles
Zero Trust approaches generally avoid automatically trusting users or devices based solely on their network location. Access decisions can instead consider identity, device status, context and other relevant signals.
Benefits of Adaptive Network Control
A flexible network control strategy can help organisations respond to security events while maintaining greater visibility across changing environments.
Faster Threat Response
Automated monitoring and predefined responses can reduce the time required to address certain security events.
Improved Network Visibility
Continuous monitoring can provide security teams with greater insight into devices, users, applications and traffic patterns.
Reduced Attack Exposure
When suspicious activity is detected, appropriate restrictions can help limit access to sensitive systems or resources.
Support for Distributed Networks
Adaptive controls can be useful in environments that include cloud services, remote workers, multiple offices and connected devices.
Improved Security Efficiency
Automation can reduce the need for security teams to manually perform repetitive tasks, allowing them to focus on investigations and more complex security decisions.
Examples of Adaptive Network Control in Practice
The practical value of adaptive network control becomes clearer when considering how security policies can respond to specific changes in network behaviour.
Suspicious Device Activity
Suppose an internal device begins communicating with systems it has never previously contacted and generates an unusual volume of traffic.
An adaptive control system could identify the change and apply a predefined response, such as increasing monitoring or restricting certain network connections.
Compromised User Account
An account may normally be used from a particular location during standard working hours but suddenly attempts multiple unusual access requests.
Depending on the organisation's policies, adaptive controls could require additional authentication or restrict access until the activity has been reviewed.
Unusual Network Traffic
A sudden change in traffic volume or communication patterns can be investigated as a potential security event.
Adaptive controls can help apply predefined measures while security teams determine whether the activity is legitimate or malicious.
Emerging Cyber Threat
When security teams receive reliable intelligence about a new threat, they can update relevant network policies to address associated indicators or behaviours.
This allows security controls to evolve as the threat environment changes.
Adaptive Network Control vs Traditional Network Control
The main distinction between adaptive and traditional network control is how security policies respond when network conditions change.
Traditional approaches often depend heavily on predefined rules that remain in place until an administrator manually changes them.
Adaptive approaches can use continuous information about users, devices, traffic and security events to support dynamic decisions.
The difference can be considered across several areas:
Policy: Fixed rules compared with policies that can change according to defined conditions.
Monitoring: Periodic or event-based checks compared with continuous monitoring.
Response: Manual intervention compared with automated responses for selected events.
Access decisions: Decisions based mainly on predefined permissions compared with decisions that can incorporate contextual risk.
Management: Static configurations compared with continuously reviewed security controls.
Neither approach eliminates the need for security governance. Adaptive systems still require clear policies, testing and human oversight.
Challenges of Implementing Adaptive Network Control
Although adaptive controls can improve responsiveness, organisations must manage several technical and operational challenges.
Integration With Existing Infrastructure
New adaptive technologies may need to work with existing network, endpoint, identity and security systems.
Policy Complexity
Large environments can require many rules and conditions. Poorly designed policies may create unnecessary complexity or inconsistent behaviour.
False Positives
Not every unusual activity is malicious. Incorrectly identifying legitimate behaviour as suspicious could interrupt business operations.
Data Quality
Adaptive decisions depend on the quality and availability of monitoring information. Incomplete or inaccurate data can affect the reliability of security decisions.
Staff Skills
Security teams need appropriate knowledge to configure, monitor and review adaptive systems.
Business Continuity
Automated security actions should be carefully designed so that legitimate users and critical services are not unnecessarily disrupted.
Best Practices for Implementing Adaptive Network Control
A carefully planned implementation can help organisations gain the benefits of adaptive controls while reducing unnecessary operational disruption.
Businesses can consider several practices:
Define clear security objectives: Determine which risks the adaptive controls are intended to address.
Maintain accurate network visibility: Ensure relevant users, devices and systems can be monitored effectively.
Create risk-based policies: Define what actions should occur under different security conditions.
Apply least-privilege principles: Give users and devices only the access they require.
Segment critical systems: Separate sensitive resources from less critical network areas.
Test automated responses: Validate policies before deploying them widely.
Monitor policy changes: Review automated and administrator-initiated changes regularly.
Keep threat intelligence updated: Use relevant and reliable information when modifying security controls.
Maintain human oversight: Allow security professionals to review significant events and decisions.
Review the strategy regularly: Update controls as technologies, business requirements and threats evolve.
Conclusion
As network environments continue to evolve, organisations need security controls that can respond to changes rather than relying entirely on static configurations.
Adaptive network control can support this objective by combining continuous monitoring, contextual information, dynamic policies and automated responses. It can help security teams identify changes in network behaviour and apply appropriate controls based on predefined conditions.
However, adaptive controls are not a replacement for broader cybersecurity practices. Effective implementation requires accurate monitoring, well-designed policies, regular testing and appropriate human oversight.
As threats and network environments continue to change, organisations can regularly review their security controls to ensure they remain aligned with current risks and operational requirements. For more insights into cybersecurity, network protection and emerging security practices, Security Journal UK provides industry-focused information for security professionals and organisations.
Frequently Asked Questions
What is adaptive network control?
Adaptive network control is an approach in which network security policies and controls can adjust according to changing network conditions, user behaviour, device status and security risks.
How does adaptive network control respond to cyber threats?
It can continuously monitor network activity, identify predefined indicators of risk and trigger appropriate responses, such as increased monitoring, access restrictions or device isolation.
What technologies support adaptive network control?
Technologies can include network monitoring, traffic analysis, identity and access management, endpoint security, security information and event management, network segmentation and automation platforms.
What is the difference between adaptive and traditional network control?
Traditional network control often relies on fixed rules that require manual changes, while adaptive network control can use current information and predefined conditions to adjust security policies dynamically.
Can adaptive network control automate threat responses?
Yes, selected responses can be automated when organisations have clearly defined policies. Examples may include restricting access, isolating devices or requiring additional authentication.
What are the challenges of implementing adaptive network control?
Challenges can include integration with existing systems, complex policies, false positives, data quality issues, staff training and the possibility of disrupting legitimate network activity.